 English
 Italiano
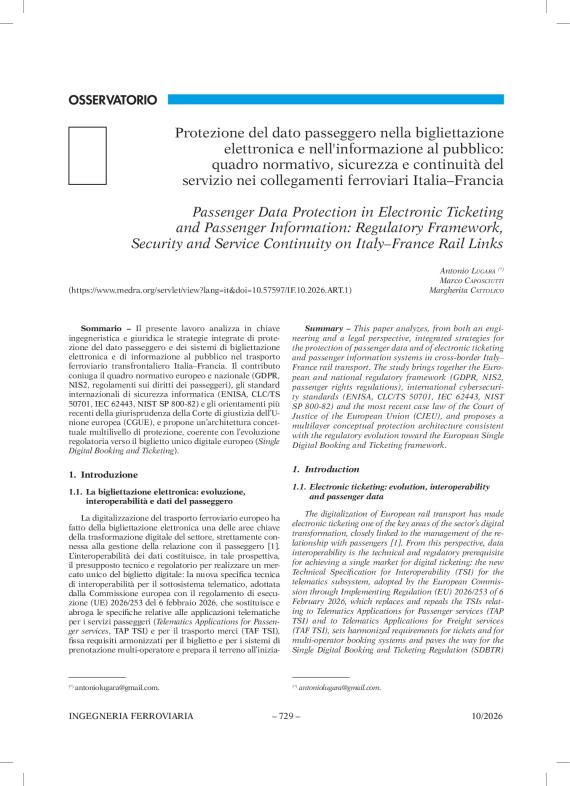
Summary – This paper analyzes, from both an engineering and a legal perspective, integrated strategies for the protection of passenger data and of electronic ticketing
and passenger information systems in cross-border Italy–France rail transport. The study brings together the European and national regulatory framework (GDPR, NIS2, passenger rights regulations), international cybersecurity standards (ENISA, CLC/TS 50701, IEC 62443, NIST SP 800-82) and the most recent case law of the Court of Justice of the European Union (CJEU), and proposes a multilayer conceptual protection architecture consistent with the regulatory evolution toward the European Single
Digital Booking and Ticketing framework.
https://www.medra.org/servlet/view?lang=it&doi=10.57597/IF.10.2026.ART.1
- Ottobre